
Exam Security-Operations-Engineer Topic 2 Question 105 Discussion
Actual exam question for Google's Security-Operations-Engineer exam
Question #: 105
Topic #: 2
Question #: 105
Topic #: 2
You are implementing Google Security Operations (SecOps) for your organization. Your organization has their own threat intelligence feed that has been ingested to Google SecOps by using a native integration with a Malware Information Sharing Platform (MISP). You are working on the following detection rule to leverage the command and control (C2) indicators that were ingested into the entity graph.
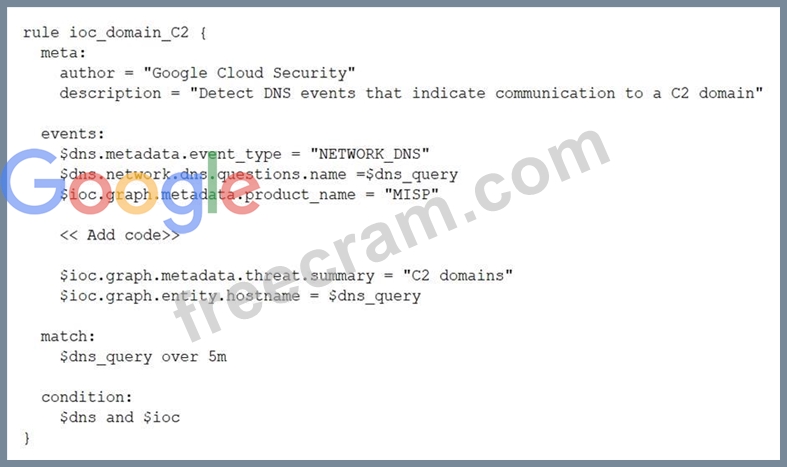
What code should you add in the detection rule to filter for the domain IOCs?
What code should you add in the detection rule to filter for the domain IOCs?
Suggested Answer: A Vote an answer
This code ensures your rule matches IOCs classified as domain names and sourced directly as entity context from MISP, allowing precise correlation between DNS queries and known C2 domains.
by Martin at May 25, 2026, 03:47 AM
0
0
0
10
Comments
Upvoting a comment with a selected answer will also increase the vote count towards that answer by one. So if you see a comment that you already agree with, you can upvote it instead of posting a new comment.
Report Comment
Commenting
You can sign-up / login (it's free).