
Exam SecOps-Pro Topic 1 Question 39 Discussion
Actual exam question for Palo Alto Networks's SecOps-Pro exam
Question #: 39
Topic #: 1
Question #: 39
Topic #: 1
Consider the following pseudo-code for an alert correlation engine designed to identify potential credential stuffing attacks against an application protected by a Palo Alto Networks firewall and Prisma Access for remote users:
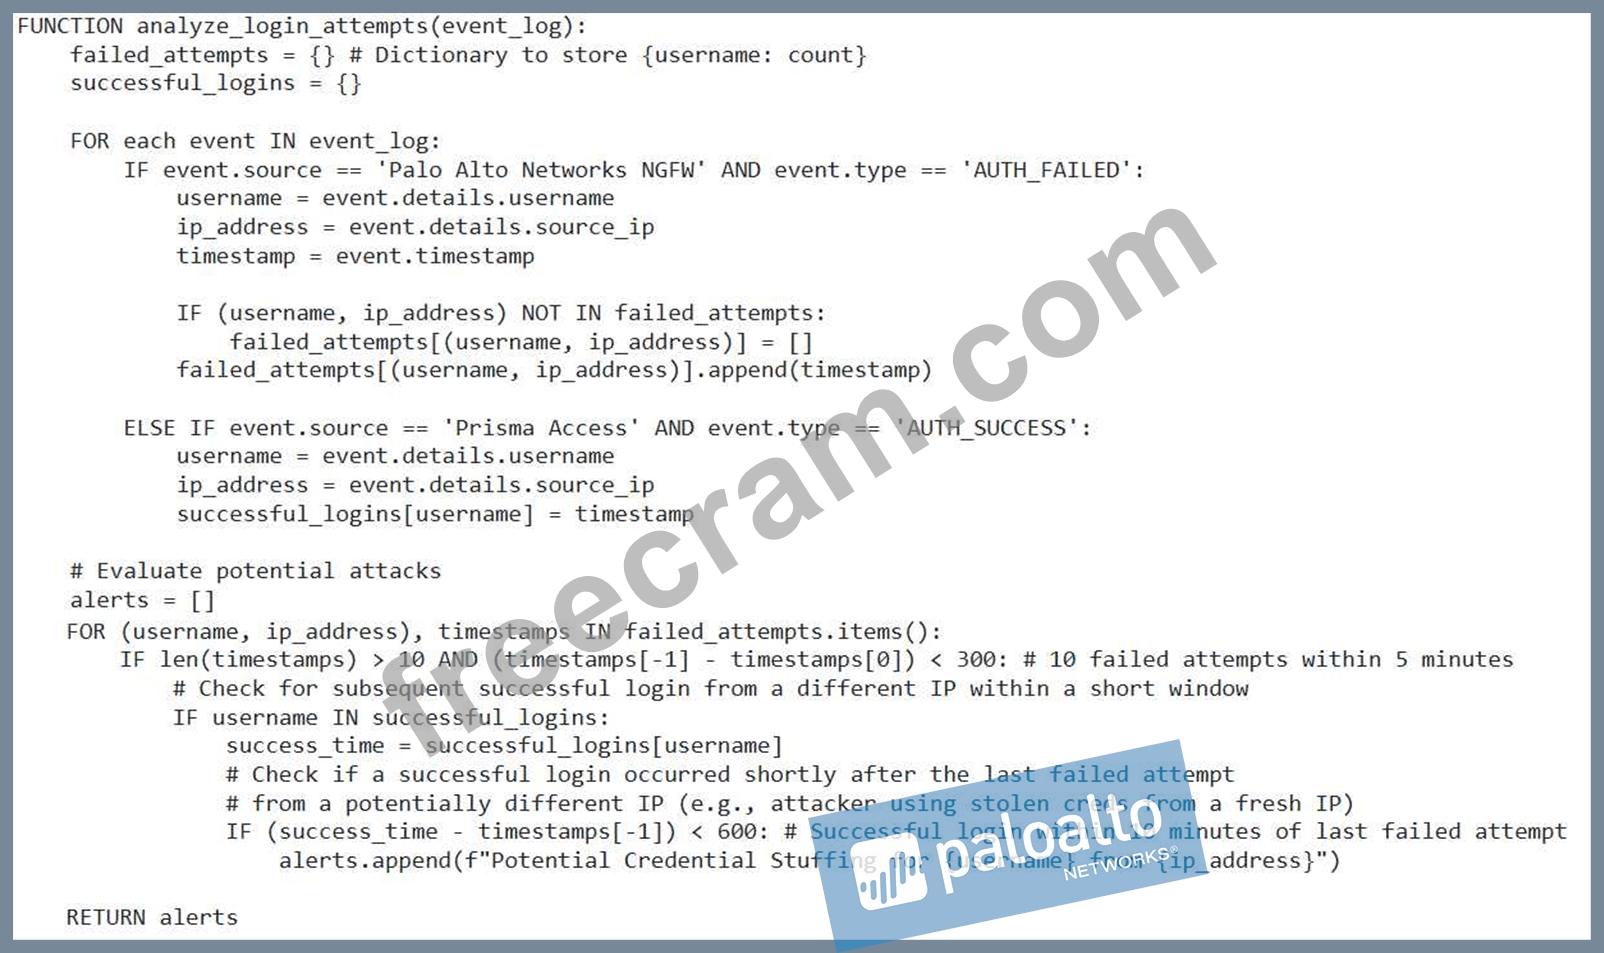
Given this logic, which of the following scenarios would most likely result in a False Positive alert, and why?
Given this logic, which of the following scenarios would most likely result in a False Positive alert, and why?
Suggested Answer: A,E Vote an answer
This question requires careful analysis of the provided pseudo-code logic. Option A (False Positive): If a user repeatedly mistypes their password (e.g., 12 times) within 5 minutes from their legitimate VPN IP, the 'len(timestamps) > 10' condition is met. If they then successfully log in from the same IP within 10 minutes, the 'username in successful_logins' and '(success_time - timestamps[-l]) < 600' conditions will also be met. The logic doesn't differentiate between the source IP of the failed attempts and the successful login's source IP for the final alert generation. This is a common user error, not a credential stuffing attack, leading to a False Positive. Option B (True Positive): An attacker changing IPs and then succeeding is a classic credential stuffing scenario. The logic could detect this if the successful login from the new IP happens within the '600' second window after the last failed attempt for that 'username'. This would be a True Positive, so the statement that it correctly identifies it is accurate. Option C (True Negative): If only failed attempts occur without a subsequent successful login, the 'IF username IN successful_logins' condition prevents an alert. This correctly reflects a scenario where no credential stuffing succeeded, even with numerous failures. This is a True Negative. Option D (True Positive): This is a very strong indicator of credential stuffing. The logic, as designed, should catch this. The 'successful_logins' dictionary only tracks the username and timestamp, not the IP for success. However, the initial 'failed_attempts' is keyed by ' (username, If the same username has a successful login after failures, regardless of the success IP, an alert is generated. This would be a correct detection. Option E (False Positive): This is a critical flaw leading to a False Positive. The 'failed_attempts' dictionary is keyed by ' (username, , which is good. However, the 'successful_logins' dictionary only stores username' and 'timestamp'. When checking username IN successful_logins:', it doesn't verify if the successful login came from the same IP as the series of failed attempts. If Alice fails from IP 'X' and Bob successfully logs in (for himself) from IP 'Y', and Bob's 'successful_login' timestamp for his login (not Alice's) coincidentally falls within the '600' second window relative to Alice's last failed attempt, the alert '"Potential Credential Stuffing for Alice from IP would be generated, which is incorrect. This is a False Positive because the success is unrelated to the failures. The key issue is the lack of IP correlation for successful logins in the detection logic. Therefore, A and E are the scenarios most likely to result in False Positives based on the provided code.
by Herman at Sep 17, 2026, 04:31 PM
0
0
0
10
Comments
Upvoting a comment with a selected answer will also increase the vote count towards that answer by one. So if you see a comment that you already agree with, you can upvote it instead of posting a new comment.
Report Comment
Commenting
You can sign-up / login (it's free).