

Exam Questions Answers Braindumps NSE4_FGT-7.0 Exam Dumps PDF Questions
Download Free Fortinet NSE4_FGT-7.0 Real Exam Questions
Fortinet NSE4_FGT-7.0 (Fortinet NSE 4 - FortiOS 7.0) certification exam is a highly sought-after certification exam in the field of cybersecurity. Fortinet NSE 4 - FortiOS 7.0 certification exam validates the knowledge and skills required to configure and manage FortiGate firewalls for day-to-day operations in an enterprise environment. NSE4_FGT-7.0 exam is designed to assess the candidate’s ability to install, configure, and troubleshoot FortiGate devices in both standalone and distributed configurations.
NEW QUESTION # 63
Refer to the exhibit.
Which contains a Performance SLA configuration.
An administrator has configured a performance SLA on FortiGate. Which failed to generate any traffic. Why is FortiGate not generating any traffic for the performance SLA?
- A. The Ping protocol is not supported for the public servers that are configured.
- B. You need to turn on the Enable probe packets switch.
- C. There may not be a static route to route the performance SLA traffic.
- D. Participants configured are not SD-WAN members.
Answer: B
NEW QUESTION # 64
Which two statements about SSL VPN between two FortiGate devices are true? (Choose two.)
- A. The client FortiGate requires a client certificate signed by the CA on the server FortiGate.
- B. The client FortiGate requires a manually added route to remote subnets.
- C. Server FortiGate requires a CA certificate to verify the client FortiGate certificate.
- D. The client FortiGate uses the SSL VPN tunnel interface type to connect SSL VPN.
Answer: B,D
Explanation:
Explanation
https://docs.fortinet.com/document/fortigate/6.2.9/cookbook/266506/ssl-vpn-with-certificateauthentication
NEW QUESTION # 65
An administrator has a requirement to keep an application session from timing out on port 80. What two changes can the administrator make to resolve the issue without affecting any existing services running through FortiGate? (Choose two.)
- A. Set the session TTL on the HTTP policy to maximum
- B. Set the TTL value to never under config system-ttl
- C. Create a new service object for HTTP service and set the session TTL to never
- D. Create a new firewall policy with the new HTTP service and place it above the existing HTTP policy.
Answer: C,D
Explanation:
https://community.fortinet.com/t5/FortiGate/Technical-Tip-Session-timeout-settings/ta-p/191228
NEW QUESTION # 66
An administrator needs to increase network bandwidth and provide redundancy.
What interface type must the administrator select to bind multiple FortiGate interfaces?
- A. Redundant interface
- B. VLAN interface
- C. Software Switch interface
- D. Aggregate interface
Answer: D
NEW QUESTION # 67
A network administrator wants to set up redundant IPsec VPN tunnels on FortiGate by using two IPsec VPN tunnels and static routes.
* All traffic must be routed through the primary tunnel when both tunnels are up
* The secondary tunnel must be used only if the primary tunnel goes down
* In addition, FortiGate should be able to detect a dead tunnel to speed up tunnel failover Which two key configuration changes are needed on FortiGate to meet the design requirements? (Choose two,)
- A. Enable Auto-negotiate and Autokey Keep Alive on the phase 2 configuration of both tunnels.
- B. Enable Dead Peer Detection.
- C. Configure a lower distance on the static route for the primary tunnel, and a higher distance on the static route for the secondary tunnel.
- D. Configure a high distance on the static route for the primary tunnel, and a lower distance on the static route for the secondary tunnel.
Answer: B,C
Explanation:
B - because the customer requires the tunnels to notify when a tunnel goes down. DPD is designed for that purpose. To send a packet over a firewall to determine a failover for the next tunnel after a specific amount of time of not receiving a response from its peer.
C - remember when it comes to choosing a route with regards to Administrative Distance. The route with the lowest distance for that particular route will be chosen. So, by configuring a lower routing distance on the primary tunnel, means that the primary tunnel will be chosen to route packets towards their destination.
NEW QUESTION # 68
If the Issuer and Subject values are the same in a digital certificate, which type of entity was the certificate issued to?
- A. A subordinate CA
- B. A root CA
- C. A person
- D. A CRL
Answer: B
NEW QUESTION # 69
Which three statements are true regarding session-based authentication? (Choose three.)
- A. It is not recommended if multiple users are behind the source NAT
- B. It can differentiate among multiple clients behind the same source IP address.
- C. It requires more resources.
- D. HTTP sessions are treated as a single user.
- E. IP sessions from the same source IP address are treated as a single user.
Answer: A,B,D
Explanation:
FortiGate_Infrastructure_6.4 page 387
NEW QUESTION # 70
An administrator must disable RPF check to investigate an issue.
Which method is best suited to disable RPF without affecting features like antivirus and intrusion prevention system?
- A. Enable asymmetric routing at the interface level.
- B. Disable the RPF check at the FortiGate interface level for the reply check.
- C. Enable asymmetric routing, so the RPF check will be bypassed.
- D. Disable the RPF check at the FortiGate interface level for the source check.
Answer: D
NEW QUESTION # 71
In which two ways can RPF checking be disabled? (Choose two )
- A. Enable anti-replay in firewall policy.
- B. Disable strict-arc-check under system settings.
- C. Disable the RPF check at the FortiGate interface level for the source check
- D. Enable asymmetric routing.
Answer: B,D
NEW QUESTION # 72
An administrator does not want to report the logon events of service accounts to FortiGate. What setting on the collector agent is required to achieve this?
- A. Add the support of NTLM authentication.
- B. Add user accounts to the FortiGate group fitter.
- C. Add user accounts to Active Directory (AD).
- D. Add user accounts to the Ignore User List.
Answer: D
NEW QUESTION # 73
A network administrator has enabled SSL certificate inspection and antivirus on FortiGate. When downloading an EICAR test file through HTTP, FortiGate detects the virus and blocks the file. When downloading the same file through HTTPS, FortiGate does not detect the virus and the file can be downloaded.
What is the reason for the failed virus detection by FortiGate?
- A. SSL/SSH Inspection profile is incorrect
- B. Antivirus definitions are not up to date
- C. Antivirus profile configuration is incorrect
- D. Application control is not enabled
Answer: A
Explanation:
Explanation
https traffic requires SSL decryption. Check the ssh inspection profile
NEW QUESTION # 74
A FortiGate is operating in NAT mode and configured with two virtual LAN (VLAN) sub interfaces added to the physical interface.
Which statements about the VLAN sub interfaces can have the same VLAN ID, only if they have IP addresses in different subnets.
- A. The two VLAN sub interfaces can have the same VLAN ID, only if they have IP addresses in the same subnet.
- B. The two VLAN sub interfaces can have the same VLAN ID, only if they belong to different VDOMs.
- C. The two VLAN sub interfaces can have the same VLAN ID, only if they have IP addresses in different subnets.
- D. The two VLAN sub interfaces must have different VLAN IDs.
Answer: D
Explanation:
FortiGate_Infrastructure_6.0_Study_Guide_v2-Online.pdf -> page 147
"Multiple VLANs can coexist in the same physical interface, provide they have different VLAN ID"
NEW QUESTION # 75
Refer to the exhibit.
An administrator has configured a performance SLA on FortiGate, which failed to generate any traffic.
Why is FortiGate not sending probes to 4.2.2.2 and 4.2.2.1 servers? (Choose two.)
- A. The Detection Mode setting is not set to Passive.
- B. The configured participants are not SD-WAN members.
- C. Administrator didn't configure a gateway for the SD-WAN members, or configured gateway is not valid.
- D. The Enable probe packets
Answer: C,D
NEW QUESTION # 76
Which of the following statements correctly describes FortiGates route lookup behavior when searching for a suitable gateway? (Choose two)
- A. Lookup is done on the last packet sent from the responder
- B. Lookup is done on the first packet from the session originator
- C. Lookup is done on every packet, regardless of direction
- D. Lookup is done on the trust reply packet from the responder
Answer: B,D
NEW QUESTION # 77
Examine this PAC file configuration.
Which of the following statements are true? (Choose two.)
- A. Any web request fortinet.com is allowed to bypass the proxy.
- B. Any web request to the 172.25.120.0/24 subnet is allowed to bypass the proxy.
- C. Browsers can be configured to retrieve this PAC file from the FortiGate.
- D. All requests not made to Fortinet.com or the 172.25.120.0/24 subnet, have to go through altproxy.corp.com: 8060.
Answer: A,C
NEW QUESTION # 78
Refer to the web filter raw logs.
Based on the raw logs shown in the exhibit, which statement is correct?
- A. The action on firewall policy ID 1 is set to warning.
- B. Access to the social networking web filter category was explicitly blocked to all users.
- C. Social networking web filter category is configured with the action set to authenticate.
- D. The name of the firewall policy is all_users_web.
Answer: C
NEW QUESTION # 79
An administrator wants to configure Dead Peer Detection (DPD) on IPSEC VPN for detecting dead tunnels. The requirement is that FortiGate sends DPD probes only when no traffic is observed in the tunnel.
Which DPD mode on FortiGate will meet the above requirement?
- A. Disabled
- B. Enabled
- C. On Demand
- D. On Idle
Answer: D
NEW QUESTION # 80
Examine the IPS sensor and DoS policy configuration shown in the exhibit, then answer the question below.
When detecting attacks, which anomaly, signature, or filter will FortiGate evaluate first?
- A. SMTP.Login.Brute.Force
- B. IMAP.Login.brute.Force
- C. Location: server Protocol: SMTP
- D. ip_src_session
Answer: B
NEW QUESTION # 81
Examine the following web filtering log.
Which statement about the log message is true?
- A. The action for the category Games is set to block.
- B. The web site miniclip.com matches a static URL filter whose action is set to Warning.
- C. The usage quota for the IP address 10.0.1.10 has expired
- D. The name of the applied web filter profile is default.
Answer: D
NEW QUESTION # 82
An administrator observes that the port1 interface cannot be configured with an IP address. What can be the reasons for that? (Choose three.)
- A. The interface is a member of a zone.
- B. The interface has been configured for one-arm sniffer.
- C. Captive portal is enabled in the interface.
- D. The interface is a member of a virtual wire pair.
- E. The operation mode is transparent.
Answer: B,D,E
Explanation:
Explanation
https://help.fortinet.com/fos50hlp/54/Content/FortiOS/fortigate-whats-new-54/Top_VirtualWirePair.htm
NEW QUESTION # 83
Refer to the exhibit.

The exhibit contains the configuration for an SD-WAN Performance SLA, as well as the output of diagnose sys virtual-wan-link health-check.
Which interface will be selected as an outgoing interface?
- A. port2
- B. port1
- C. port4
- D. port3
Answer: B
Explanation:
Port 1 shows the lowest latency.
NEW QUESTION # 84
Refer to the exhibit, which contains a session diagnostic output.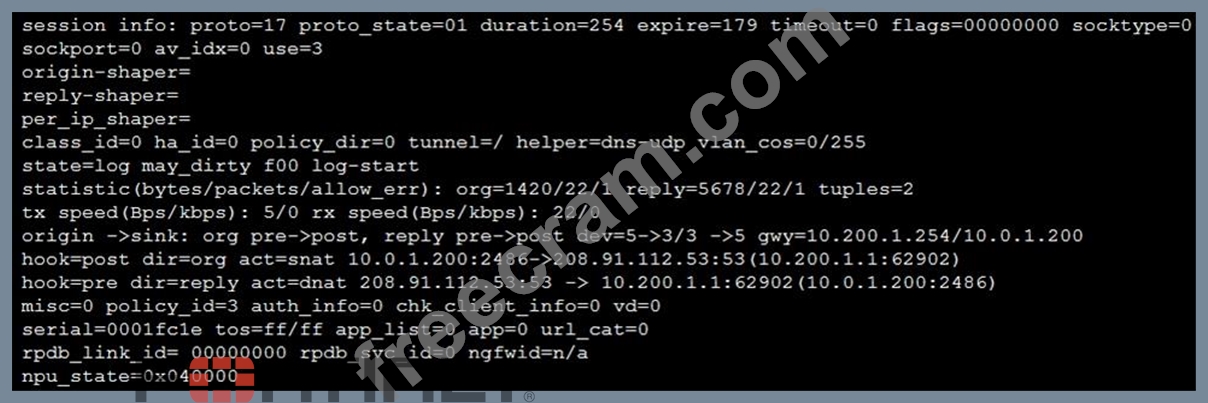
Which statement is true about the session diagnostic output?
- A. The session is a UDP unidirectional state.
- B. The session is a bidirectional TCP connection.
- C. The session is in TCP ESTABLISHED state.
- D. The session is a bidirectional UDP connection.
Answer: D
NEW QUESTION # 85
Which of the following are purposes of NAT traversal in IPsec? (Choose two.)
- A. To dynamically change phase 1 negotiation mode aggressive mode.
- B. To detect intermediary NAT devices in the tunnel path.
- C. To force a new DH exchange with each phase 2 rekey.
- D. To encapsulation ESP packets in UDP packets using port 4500.
Answer: B,D
Explanation:
Explanation
https://kb.fortinet.com/kb/documentLink.do?externalID=FD48755
NEW QUESTION # 86
......
Fortinet NSE4_FGT-7.0 certification exam is intended for network security professionals who work with Fortinet products and services. It is particularly suitable for those who are responsible for deploying, configuring, and maintaining Fortinet's FortiOS 7.0 operating system. NSE4_FGT-7.0 exam is also a valuable credential for individuals who want to advance their careers in the field of network security. By demonstrating their knowledge and proficiency in using FortiOS 7.0, certified professionals can prove their expertise and increase their employability.
Latest Fortinet NSE4_FGT-7.0 Real Exam Dumps PDF: https://www.freecram.com/Fortinet-certification/NSE4_FGT-7.0-exam-dumps.html
NSE4_FGT-7.0 Exam Dumps, NSE4_FGT-7.0 Practice Test Questions: https://drive.google.com/open?id=1WabW4yI4aqJEKcM4Ay8WKUYc5jCQrOh1