

Updated Apr-2024 Official licence for SC-100 Certified by SC-100 Dumps PDF
Grab latest Amazon SC-100 Dumps as PDF Updated on 2024
Microsoft SC-100 certification exam is a great way to validate your expertise in cybersecurity architecture and risk management. SC-100 exam consists of multiple-choice questions and is designed to test the candidate’s knowledge and skills in various cybersecurity domains. SC-100 exam is intended for cybersecurity professionals who want to enhance their knowledge and skills and demonstrate their expertise to potential employers.
NEW QUESTION # 10
Your company uses Microsoft Defender for Cloud and Microsoft Sentinel. The company is designing an application that will have the architecture shown in the following exhibit.
You are designing a logging and auditing solution for the proposed architecture. The solution must meet the following requirements-.
* Integrate Azure Web Application Firewall (WAF) logs with Microsoft Sentinel.
* Use Defender for Cloud to review alerts from the virtual machines.
What should you include in the solution? To answer, select the appropriate options in the answer are
a. NOTE: Each correct selection is worth one point.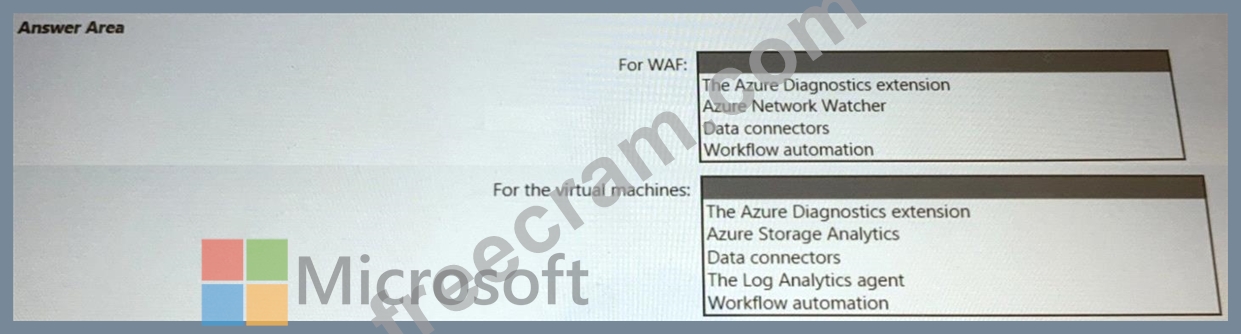
Answer:
Explanation:
NEW QUESTION # 11
You are creating the security recommendations for an Azure App Service web app named App1.
App1 has the following specifications:
* Users will request access to App1 through the My Apps portal. A human resources manager will approve the requests.
* Users will authenticate by using Azure Active Directory (Azure AD) user accounts.
You need to recommend an access security architecture for App1.
What should you include in the recommendation? To answer, select the appropriate options in the answer are a. NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 12
You need to recommend an identity security solution for the Azure AD tenant of Litware. The solution must meet the identity requirements and the regulatory compliance requirements.
What should you recommend? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 13
You need to recommend an identity security solution for the Azure AD tenant of Litware. The solution must meet the identity requirements and the regulatory compliance requirements.
What should you recommend? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 14
You have a customer that has a Microsoft 365 subscription and an Azure subscription.
The customer has devices that run either Windows, iOS, Android, or macOS. The Windows devices are deployed on-premises and in Azure.
You need to design a security solution to assess whether all the devices meet the customer's compliance rules.
What should you include in the solution?
- A. Microsoft Endpoint Manager
- B. Microsoft Sentinel
- C. Microsoft Information Protection
- D. Microsoft Defender for Endpoint
Answer: A
NEW QUESTION # 15
Your company has a Microsoft 365 subscription and uses Microsoft Defender for Identity. You are informed about incidents that relate to compromised identities.
You need to recommend a solution to expose several accounts for attackers to exploit. When the attackers attempt to exploit the accounts, an alert must be triggered. Which Defender for Identity feature should you include in the recommendation?
- A. honeytoken entity tags
- B. standalone sensors
- C. sensitivity labels
- D. custom user tags
Answer: D
NEW QUESTION # 16
You have an Azure subscription that has Microsoft Defender for Cloud enabled. You are evaluating the Azure Security Benchmark V3 report.
In the Secure management ports controls, you discover that you have 0 out of a potential 8 points. You need to recommend configurations to increase the score of the Secure management ports controls.
Solution: You recommend onboarding all virtual machines to Microsoft Defender for Endpoint.
Does this meet the goal?
- A. No
- B. Yes
Answer: A
Explanation:
Explanation
https://docs.microsoft.com/en-us/azure/defender-for-cloud/secure-score-security-controls
NEW QUESTION # 17
You are evaluating the security of ClaimsApp.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE; Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 18
Your company has Microsoft 365 E5 licenses and Azure subscriptions.
The company plans to automatically label sensitive data stored in the following locations:
* Microsoft SharePoint Online
* Microsoft Exchange Online
* Microsoft Teams
You need to recommend a strategy to identify and protect sensitive data.
Which scope should you recommend for the sensitivity label policies? To answer, drag the appropriate scopes to the correct locations. Each scope may be used once, more than once, or not at all. You may need to drag the split bar between panes or scroll to view content.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 19
You have a Microsoft 365 subscription.
You are designing a user access solution that follows the Zero Trust principles of the Microsoft Cybersecurity Reference Architectures (MCRA).
You need to recommend a solution that automatically restricts access to Microsoft Exchange Online.
SharePoint Online, and Teams m near-real-lime (NRT) in response to the following Azure AD events:
* A user account is disabled or deleted
* The password of a user is changed or reset.
* All the refresh tokens for a user are revoked
* Multi-factor authentication (MFA) is enabled for a user
Which two features should you include in the recommendation? Each correct answer presents part of the solution. NOTE: Each correct selection is worth one point.
- A. Conditional Access
- B. Azure AD Privileged Identity Management (PIM)
- C. a sign-in risk policy
- D. Azure AD Application Proxy
- E. continuous access evaluation
Answer: A,E
NEW QUESTION # 20
Your company plans to move all on-premises virtual machines to Azure. A network engineer proposes the Azure virtual network design shown in the following table.
You need to recommend an Azure Bastion deployment to provide secure remote access to all the virtual machines. Based on the virtual network design, how many Azure Bastion subnets are required?
- A. 0
- B. 1
- C. 2
- D. 3
- E. 4
Answer: B
Explanation:
Explanation
https://docs.microsoft.com/en-us/azure/bastion/vnet-peering
https://docs.microsoft.com/en-us/learn/modules/connect-vm-with-azure-bastion/2-what-is-azure-bastion
NEW QUESTION # 21
You need to recommend a SIEM and SOAR strategy that meets the hybrid requirements, the Microsoft Sentinel requirements, and the regulatory compliance requirements.
What should you recommend? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 22
You have a customer that has a Microsoft 365 subscription and uses the Free edition of Azure Active Directory (Azure AD)
The customer plans to obtain an Azure subscription and provision several Azure resources.
You need to evaluate the customer's security environment.
What will necessitate an upgrade from the Azure AD Free edition to the Premium edition?
- A. role-based authorization
- B. Azure AD Multi-Factor Authentication
- C. resource-based authorization
- D. Azure AD Privileged Identity Management (PIM)
Answer: A
NEW QUESTION # 23
You have a Microsoft 365 E5 subscription and an Azure subscripts You need to evaluate the existing environment to increase the overall security posture for the following components:
* Windows 11 devices managed by Microsoft Intune
* Azure Storage accounts
* Azure virtual machines
What should you use to evaluate the components? To answer, select the appropriate options in the answer area.
Answer:
Explanation:
NEW QUESTION # 24
Your network contains an on-premises Active Directory Domain Services (AO DS) domain. The domain contains a server that runs Windows Server and hosts shared folders The domain syncs with Azure AD by using Azure AD Connect Azure AD Connect has group writeback enabled.
You have a Microsoft 365 subscription that uses Microsoft SharePoint Online.
You have multiple project teams. Each team has an AD DS group that syncs with Azure AD Each group has permissions to a unique SharePoint Online site and a Windows Server shared folder for its project. Users routinely move between project teams.
You need to recommend an Azure AD identity Governance solution that meets the following requirements:
* Project managers must verify that their project group contains only the current members of their project team
* The members of each project team must only have access to the resources of the project to which they are assigned
* Users must be removed from a project group automatically if the project manager has MOT verified the group s membership for 30 days.
* Administrative effort must be minimized.
What should you include in the recommendation? To answer select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Explanation:
NEW QUESTION # 25
......
Latest SC-100 Exam Dumps Microsoft Exam from Training: https://www.freecram.com/Microsoft-certification/SC-100-exam-dumps.html
Newly Released SC-100 Dumps for Microsoft Certified: Cybersecurity Architect Expert Certified: https://drive.google.com/open?id=1S37bmh3BMAZqyCOWYB56tmab8pCQcwj0